
An AI readiness checklist tells you whether your Microsoft 365 is safe to connect AI to. It covers who can access what, where your information lives, whether confidential files are protected, which AI tools are already in use, and whether you have written rules. If you cannot answer a question, that is the finding.
This is not an assessment. It is a checklist: a ten-minute orientation you can run at board level, as a tabletop exercise, to see where you stand and whether you need to dig deeper. You do not need an engineer to run it, and you do not need to be technical. You need to know your business, and you need to be honest about the answers.
Why does AI readiness come down to permissions?
Most firms assume their Microsoft 365 is tidier than it is. The word for what we usually find is oversharing. A project folder was shared with the whole company in 2022 and never unshared. A personal OneDrive holds half the finance team's working files, because that was easier than setting up a team site. A SharePoint folder was shared with an outside firm years ago, with no end date, and everything added to it since is still visible to them. Nobody knows who has looked at what. We find this more often than not when we onboard new clients for managed IT support in London.
Nobody notices, because people find files by clicking through to the places they know. Nobody browses to a folder they were not looking for.
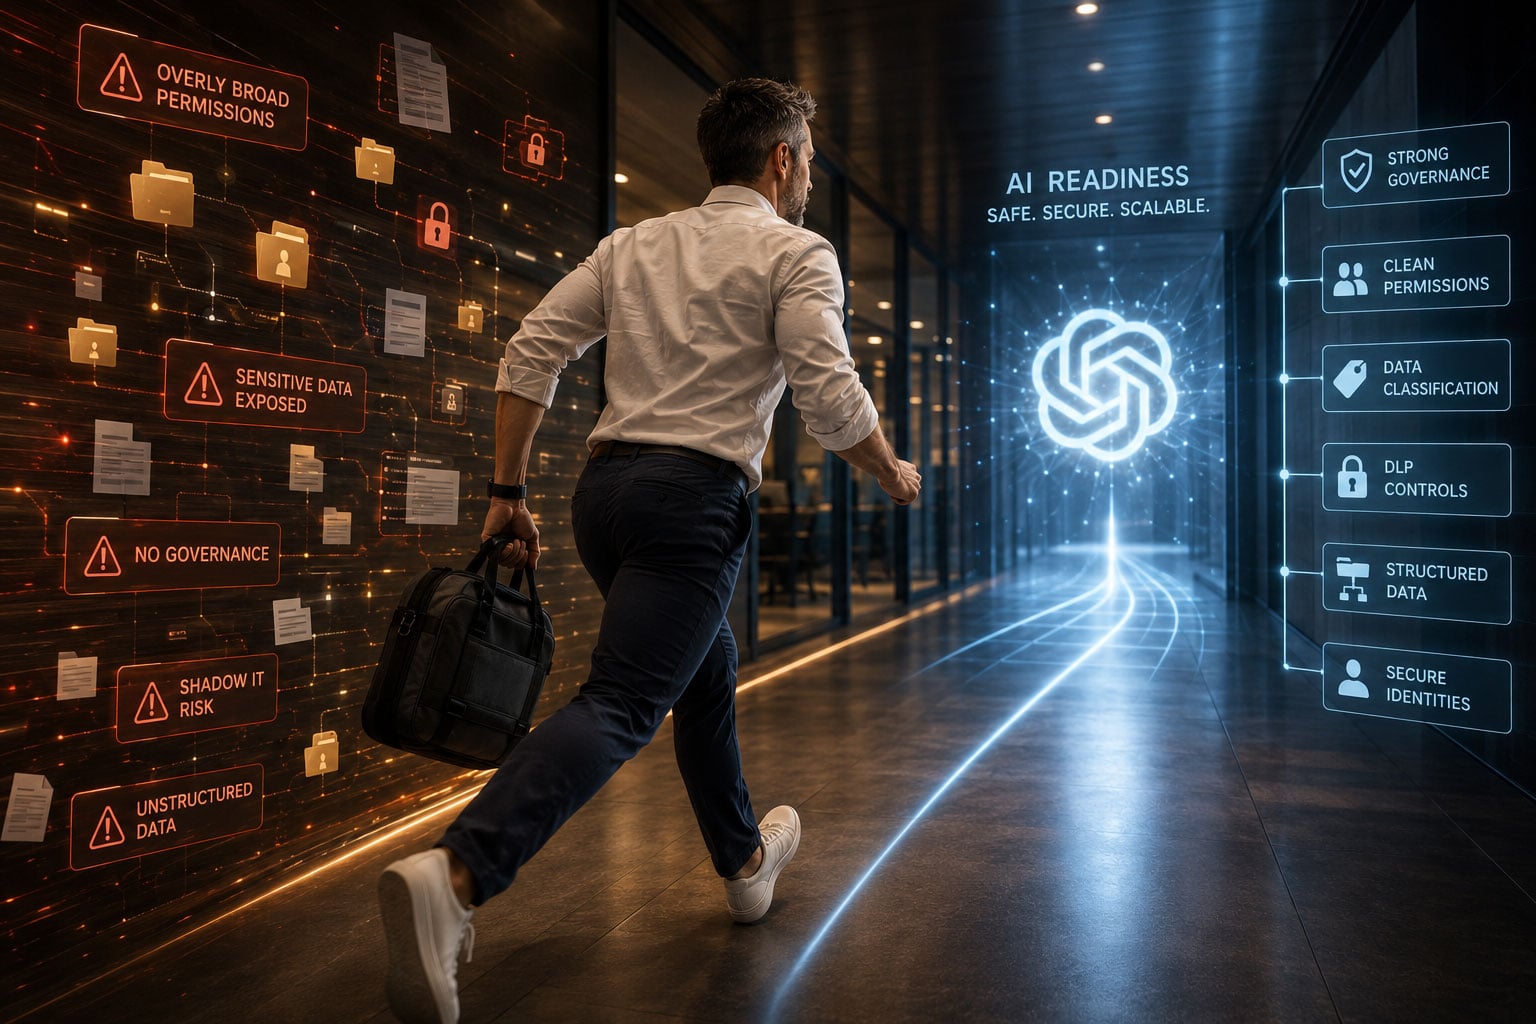
AI does not navigate. It asks and retrieves. Your tenant is your organisation's own space in Microsoft 365: its users, files, email, and settings. Point Copilot at that tenant and ask it to summarise everything on next year's salary review, and it will. It will pull from the HR folder, the board papers, and the spreadsheet a director saved to a shared drive by mistake. It will put the answer in front of whoever asked, as long as they were technically permitted to see those files. It does not know that nobody meant them to.
That is the point most readiness guides miss. AI does not create exposure in your business. It finds the exposure you already have and puts it in front of people. So readiness is mostly a question of permissions and structure, and not really a question about AI at all.
The AI readiness checklist for Microsoft 365
Ten questions. Answer each one yes, no, or don't know. Keep a tally.
- Do you know which AI tools your staff are using, including personal ChatGPT and Claude accounts?
If people are pasting client material into tools you have never approved, that is where your data is going today, before Copilot enters the picture. Yes looks like: a list of what is in use, and a view on which of those tools are fine. - Does every person's access still match their job, including leavers and people who changed role?
Access builds up. Someone who moved from finance to operations three years ago usually still has finance. Yes looks like: somebody checked within the last year, and leavers are removed the day they go. - Can you say where your confidential information actually lives: team sites, personal OneDrives, or email?
If the honest answer is "all three, and some on people's desktops", AI will treat all three as fair game. Yes looks like: the sensitive material has a known home, and people use it. - Are there sharing links to people outside the business that still work?
A folder shared with a client, a contractor, or a former employee's personal address years ago does not expire unless somebody set it to. Everything added to it since is visible to them. This is oversharing, and we can help you report on it using tools such as Microsoft Purview. Yes looks like: you have looked at the list, and anything that should have ended has been ended. - Is your most sensitive material (HR, finance, client matters, board papers) labelled so systems know it is sensitive?
A label is how Microsoft 365 tells the difference between the staff handbook and the staff salaries. Most firms need three or four: internal, confidential, highly confidential, and something for material that can go outside. Without them, every file is the same to the software. Yes looks like: your high-value areas carry a label, even if the rest of the business does not yet. - Would anything stop a confidential document being pasted into a public AI tool?
That is data loss prevention, in one sentence: a rule that notices sensitive material heading somewhere it should not and warns the person or stops it. Yes looks like: at least one rule in place for your most sensitive data. - Is multi-factor authentication on for everyone, with conditional access limiting where accounts can be used from?
AI makes a compromised account more useful to an attacker, because they can ask it questions. Yes looks like: MFA on every account with no exceptions, and sign-ins from unknown devices or countries blocked. It is the baseline in our managed cyber security services, and one of the first things cyber insurers now require. - Do you know who has Copilot, and has anyone checked its settings and what it can reach?
Licences get bought by individuals and departments without the board knowing, and usage-based billing is arriving, which means the cost can grow without anyone deciding it should. Copilot also has tenant-level settings that decide what it can search. Yes looks like: you know who is licensed, what it costs, and someone has been through the settings deliberately. - Is anyone building AI agents, and do you know what the ones already in play can access?
Agents are easy to create now. Some will already exist in your systems, built by well-meaning staff, and each one carries its builder's permissions wherever it goes. Yes looks like: you know how many there are, who built them, and what they can reach. - Do you have a written AI policy, an approved-tool list, and a rule that a person checks AI output before it goes to a client?
This is the one most firms skip, and it is the cheapest to fix. Yes looks like: a page or two that staff have actually read, not a forty-page document nobody opens.
Your score. Seven or more yeses and you are in good shape to proceed with care. Four to six, fix the gaps first. Three or fewer, do not switch anything on until you have had it looked at. Count every "don't know" as a no. Where the honest answer is "I don't know", that is itself the finding.
If you have more than a couple of "don't know" answers, the AI Readiness Assessment checks all ten, and more, against your actual Microsoft 365 for a fixed fee.
What is Copilot readiness, and is it different?
Copilot readiness is the same checklist applied to Microsoft's own AI, with two extras: your tenant settings and your licensing. Copilot runs inside Microsoft 365, so it works to the permissions you already have. It respects them to the letter, and that is exactly the point. Copilot data security is really permissions security: it will be as safe, or as leaky, as your permissions are.
The settings extra is question eight above. The licensing extra is simpler than people expect. You do not need a licence for everyone, and most firms of twenty to a hundred staff should not start that way. A pilot group of five to ten people who will actually use it, in a part of the business where the information is well organised, tells you far more than a company-wide rollout on day one.
If your firm runs on Google Workspace rather than Microsoft 365, the questions are the same. The names change, but what you want is a review of any oversharing, using tools such as Purview or the Google equivalents, and a clear view of what any AI tool or agent has been given access to.
What do Purview, sensitivity labels, and DLP actually do?
You will have heard these names. Here is what they mean.
Microsoft Purview is the toolkit. It is the part of Microsoft 365 that handles information protection, data governance, and compliance. Labels and data loss prevention both live inside it. If someone says "we need to look at Purview", they mean the set of controls that decide how your information is classified and protected.
Sensitivity labels mark what is sensitive. A label is a tag on a file or email that says, in effect, "this is confidential" or "this is for the board only". Once a file carries a label, the rest of the system can act on it: encrypt it, stop it being forwarded outside the business, or keep Copilot from quoting it to the wrong person.
Data loss prevention, or DLP, stops sensitive material going where it should not. It is a set of rules that watch for things like client account numbers, salary data, or anything carrying a confidential label, and either warn the person or block the action when that material is about to leave the business.
You may not need to go this far. For a firm of twenty to a hundred staff, these are options, not requirements, and the right starting point is usually not to label everything. Label the high-value areas first: finance, HR, client matters, and board papers. Set the rules to warn rather than block, so people learn what is sensitive without being stopped from doing their jobs. Blanket labelling on day one tends to generate noise, and noise gets switched off. The written policy and the approved-tool list, which cost nothing, come before any of it.
What should you do with your answers?
Treat readiness as getting your house in order: the foundation for getting value, not a brake on it. We are not anti-AI. The firms that will do best with it are not the ones that switch it on first. They are the ones with the foundations to switch it on confidently, and then to use it properly because nobody is worried about what it might say.
Three practical steps, in this order.
- Write the policy. A page or two: which tools are approved, what must never go into a public AI tool, and the rule that a person checks AI output before it goes to a client. This costs nothing, closes the most common gap on the list, and sits alongside your other information security policies.
- Fix the permissions. Start with leavers, external sharing links, and the two or three places your most sensitive material lives. Label those areas. Put a warn-only DLP rule on them. Do not try to tidy everything; tidy the parts that matter.
- Switch on for a pilot group. Five to ten people in a well-organised part of the business. Give them a month. Ask them what they used it for and what surprised them. Then decide about the rest.
If you can answer all ten with confidence, you have probably already had an assessment done and someone owns this for you. That is the position to be in. These are business questions, not IT questions, and anyone responsible for the firm, the CEO or the board, should know they have been addressed, at the very minimum to the level of this checklist.
If you cannot answer three or four of them, you have found your first project, and it is a short one. The AI Readiness Assessment goes through all of this in depth against your actual systems, with you rather than for you, so you end up with solid answers and know where you stand. Our AI consultancy work, including the policy, picks up from there.
|
|
AI readiness checklist |
AI Readiness Assessment |
|
Who does it |
You, at board level |
A senior engineer, with you and the business |
|
How long |
About ten minutes |
About a day |
|
What it checks |
What you believe the answers are |
What is actually in your Microsoft 365: permissions, sharing, labels, Copilot settings, agents, and AI tools in use |
|
What you get |
A score out of ten |
A written report with findings and what to fix first |
|
Cost |
Free |
£950 fixed for a standard Microsoft 365 environment |
Download the AI Readiness Checklist as a PDF.
Frequently asked questions
The checklist takes about ten minutes, and it tells you whether you need to look deeper. An AI Readiness Assessment takes about a day. A senior engineer looks at the actual permissions, sharing, labels, settings, and agents in your Microsoft 365, talks to you and the business about how information is used, and writes it up.
No. Start with a pilot group of five to ten people who will use it, in a part of the business where the information is well organised. Buy more licences once you know what it is being used for.
For business data, usually yes, because Copilot works inside your Microsoft 365 and to your permissions, and your data stays within your tenant rather than going to a consumer service or being used to train the AI company's models. But "safer" depends on those permissions being right. A free personal ChatGPT account with client material pasted into it is the bigger day-to-day risk in most firms, and it is question one on the list for that reason.
The checklist asks you what you think the answers are. An assessment finds out. We check far more than the ten questions here: who can see what, where information lives, how Purview, labels, and data loss prevention are set up, what Copilot and any agents can reach, and which AI tools are already in use. It is done with you, not for you, so the answers are yours and someone in the business owns them afterwards. You get a report with findings and a short list of what to fix first. For a standard Microsoft 365 environment it is a fixed fee of £950, and we can help with the policy as well.
Not in a well-run firm. The work we see AI doing well is the repetitive work people do not want: sorting a shared inbox, drafting the first version of a routine document, summarising a long thread. It gives people time back. The people who get the most from it are the ones who know the business well enough to check what it produces, which is why the policy question matters.
Find out what AI can see before you switch it on
The AI Readiness Assessment is a one-day review of your Microsoft 365 by a senior engineer. We look through your systems, talk to you and the business about how information is used, and give you a written report of what AI would surface today and what to fix first. It is £950 fixed for a standard Microsoft 365 environment. The first step is a short call to agree the scope.
Ratcliff IT is Cyber Essentials Plus certified, a Microsoft partner since 2009, and has been named one of Britain's Top 50 Best Managed IT Companies every year since 2018.
- Download the AI Readiness Checklist as a PDF.
- Book an AI Readiness Assessment
- Not sure yet? Book a no-strings discovery call with our founder James Ratcliff and we will talk it through.
- Want the wider picture first? Read our guide, AI, Automation, and the Well-Run Business.

Written by
James Ratcliff
Managing Director